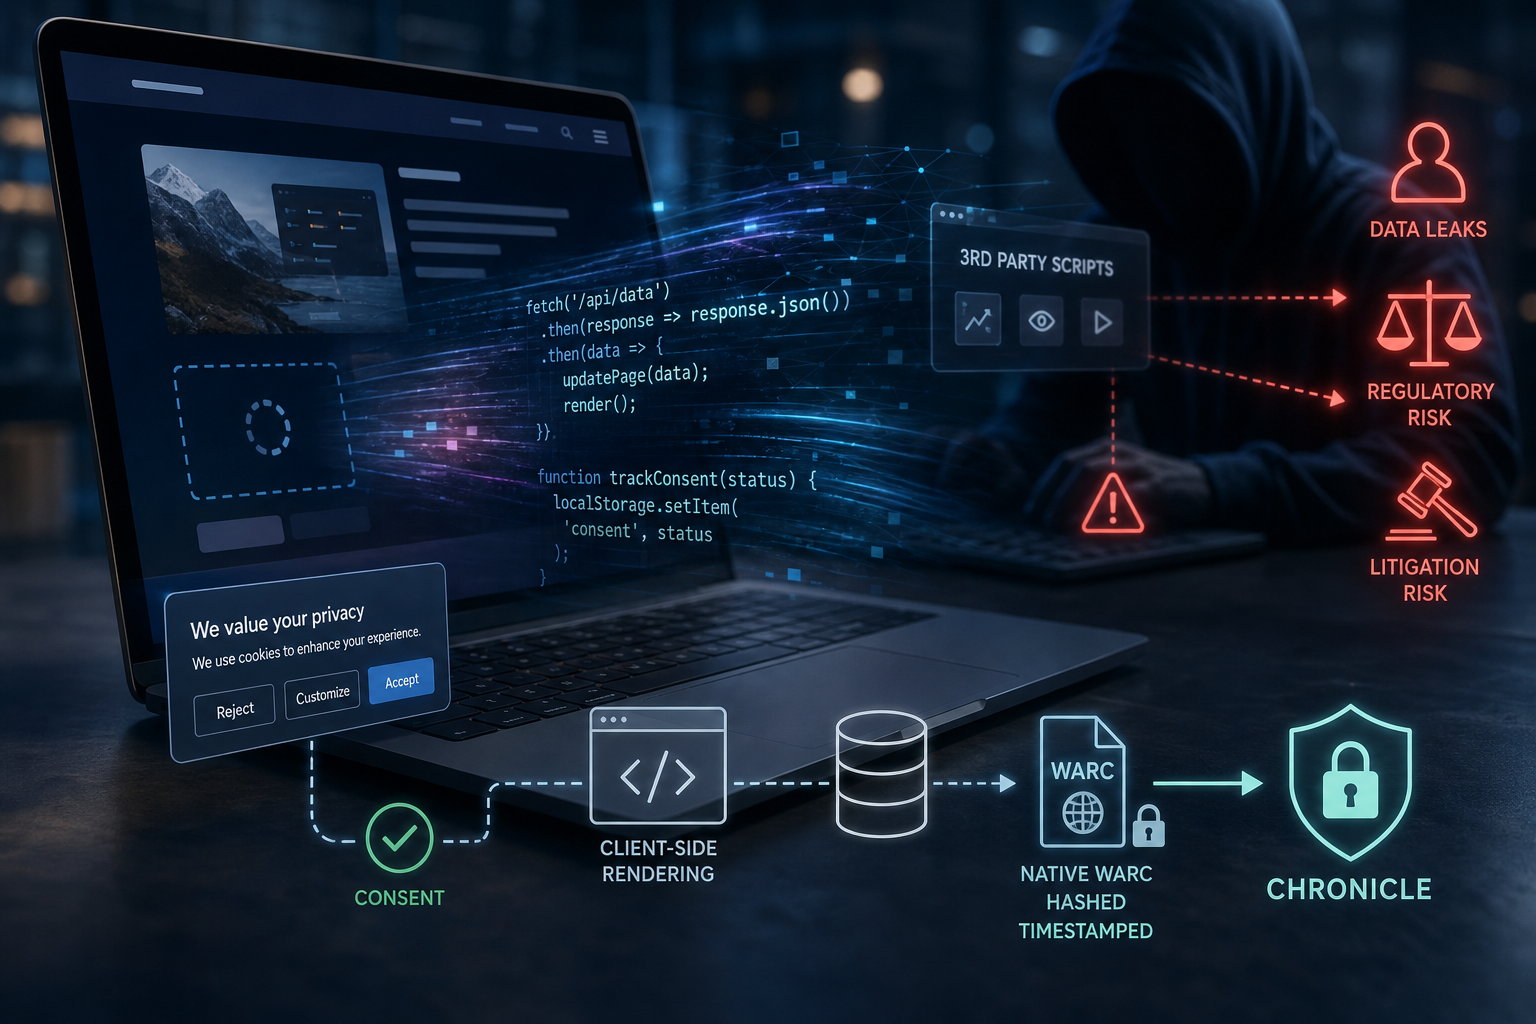
Your company needs to understand that JavaScript heavy websites, such as single-page applications (SPAs), complicate data capture. Client-side rendering could bypass corporate compliance controls, presenting serious consequences for archiving a JavaScript website, from unintentional data leaks and class-action lawsuits to regulatory investigations.
Legal and compliance teams must understand this architecture to ensure they properly vet, encrypt, and securely manage data at the client (rather than just server) level. Learn how JavaScript heavy websites complicate data capture and which Hanzo tool is best suited to your needs.
JavaScript Creates Incomplete Consent and Tracking Gaps
In traditional multi-page sites, a reload forces a new script execution, prompting a cookie banner or tracking consent check. In an SPA, users navigate through multiple views using background API calls without actually reloading the document. A visitor could interact deeply with sensitive areas, such as viewing healthcare articles or inputting information. The standard tracking scripts might not fire again, failing to capture the updated consent or verify opt-outs.
A complication of JavaScript website archiving is the risk of violating frameworks such as the GDPR, CCPA, or HIPAA. This is due to non-consensual sharing of Protected Health Information or Personally Identifiable Information (PII) with third parties.
Hidden Shadow Data Exfiltration on JavaScript Heavy Websites
JavaScript heavy sites rely on third-party libraries, such as ad networks, analytics, and session replays. Since execution happens entirely in the user’s browser, third-party code could invisibly intercept keystrokes or scrape input forms (such as lead gen or checkout pages) and then exfiltrate the captured data to external domains without the site owner’s direct knowledge. This could lead to severe civil class-action litigation under state wiretapping statutes or consumer privacy laws.
Broken Audit Trails and Record-Keeping
Modern regulatory requirements mandate that organizations preserve exact records of what they published and consented to on their websites. As SPAs serve dynamic content, taking a flat screenshot or logging static HTML URLs fails to capture the interactive state, hidden pop-ups, or user-specific data layers at a specific timestamp. The difficulty of archiving JavaScript websites leaves the organization defenseless in court or during regulatory audits when trying to prove historical terms of service, disclosures, or user-interface states.
Complex DOM-based Vulnerabilities in JavaScript Heavy Websites
Client-side rendering frequently utilizes Web Storage, a standard browser API, to store user data in the browser. This data can be manipulated locally by users or maliciously injected via cross-site scripting to create a critical web security vulnerability. Subsequently, the website’s data capture mechanism might accidentally process compromised or tainted data. Data corruption, data breaches, or compliance fines for failing to secure PII are a real risk of JavaScript heavy websites that complicate data capture.
A Real World Case File: Google LLC v. SerpApi LLC
Google’s 2025 lawsuit against SerpApi highlights a massive technical difficulty: extracting data at scale from modern, JavaScript heavy websites. The company filed its complaint in the U.S. District Court for the Northern District of California, alleging that SerpApi’s automated extraction of licensed images, real-time data, and Knowledge Panels bypasses technological protections.
Google argues that the data-scraping company violated Section 1201 of the Digital Millennium Copyright Act (DMCA) by bypassing Google’s SearchGuard security barriers at an astonishing scale. The case continues into 2026 with legal wrangling over whether bypassing bot-management tools constitutes a copyright violation under the DMCA.
How Can Chronicle Protect JavaScript Heavy Websites?
Chronicle protects organizations, overcoming the complications of accurately capturing JavaScript heavy, dynamic website data. It ensures legal compliance, mitigates risk, and preserves immutable, interactive web records that traditional archiving tools fail to capture. Chronicle’s robust functionality includes Dynamic Capture Technology that executes complex JavaScript to render websites exactly as a user experienced them. With full context playback, the software accurately records personalized customer journeys, interactive dropdowns, and dynamic API-driven content to prove compliance with FTC, FDA, and SEC/FINRA regulations. Using immutable WORM storage, Chronicle stores records in a defensible, unalterable format suitable for audits and litigation.
Talk to Hanzo About Archiving Your JavaScript Heavy Website
Understanding the complications of JavaScript website archiving is a good start. At Hanzo, we help large enterprises carry this knowledge forward into actionable steps.
Alongside Chronicle, we offer additional integrated platforms to manage enterprise data, including Illuminate and Spotlight AI. Whether your business wants to manage legal holds or quickly identify risk and reduce data review times, Hanzo has software for the task.
Request a demo or get in touch with our experts to learn more how you can take control of your dynamic data: https://Hanzo.co/contact-us/


 N/a